Service: Agent governance
Agent governance: AI adoption your security team will actually approve
Policies, ownership and risk review for AI agents, so adoption moves faster because the rules are already settled.
At a glance
Who it is for
Security, legal and business leaders who are deploying AI agents
What you get
Policies, ownership, risk assessment and audit readiness
How to start
A free 30 minute call, then a short written gap analysis
Why it matters
Governance is what lets AI adoption move faster
Many teams treat governance as the brake on AI. In our experience it works the other way. When security, legal and business owners agree up front on what AI agents may do, each new project stops being a fresh debate. Approvals get shorter, pilots reach production and the security team becomes a partner instead of a gate.
That is what we mean by AI adoption your security team will actually approve. The goal is not more paperwork. It is a small set of clear decisions made once, so everyone can move with confidence.
How we decide, in order
Business outcomes
What the agent is for, and who is accountable for it
Workflows and operating model
Where a person approves, and how the work changes
Platform, data and architecture
What the agent can reach and what it can run
The new picture
Why agents change the picture
A chatbot answers questions. An agent acts. It reads files, calls systems, sends messages and makes decisions on someone's behalf, often with little human review. That raises questions most organizations have not yet answered.
Without answers, agents multiply quietly, and the first time anyone asks is usually after something has gone sideways.
The pressure is real. Business teams can now build agents themselves, vendors are shipping agent features inside the tools you already own, and every one of them is a decision about access and accountability. Governance gives you one place to make those decisions consistently, instead of one team at a time.
What you get
What an agent governance engagement delivers
Policies
Clear, short policies for building, buying and running agents, written for the people who have to follow them. They cover what data agents may use, which actions need human approval and what is off limits.
Ownership
Every agent gets a named business owner and a technical owner, plus a simple lifecycle from request through retirement. Nothing runs without someone responsible for it.
Risk assessment
A repeatable review for agentic workflows that looks at data exposure, permissions, failure modes and the impact if an agent acts wrongly. The review scales with risk, so low risk ideas move quickly and high risk ones get the attention they deserve.
Audit readiness
An inventory of agents, plus the logs, approvals and evidence organized so you can answer an auditor, a customer or a regulator quickly and with confidence.
How we work
Built to work with your security team
We work alongside your security, privacy, legal and compliance teams, not around them. We bring practical experience from real enterprise AI rollouts, including Microsoft Copilot and agent platforms, and we adapt the framework to the tools you already use.
The result is a framework your security team helped shape and is glad to sign. That makes adoption faster, because the hardest conversations happen once, early, with the right people in the room. It also gives your leaders a straight answer when a board member, customer or auditor asks how your organization controls its AI agents.
How it works
Three steps. The first two are free.
We talk
A 30 minute use case discussion. Where you are, what is slowing you down, what you have tried.
We show you
A short written gap analysis: your top pain points, where AI fits and where it does not. Yours to keep either way.
We go deep
Discovery, use case prioritization, data and readiness assessment, tool selection, and a plan to get there.
Where to start
We begin with a free 30 minute call to understand which agents you already have, which are planned and where your concerns lie. Governance pairs naturally with an AI readiness assessment, and it makes Microsoft 365 Copilot enablement smoother because the rules are in place before access expands.
Who you work with
A team led by a former Microsoft employee
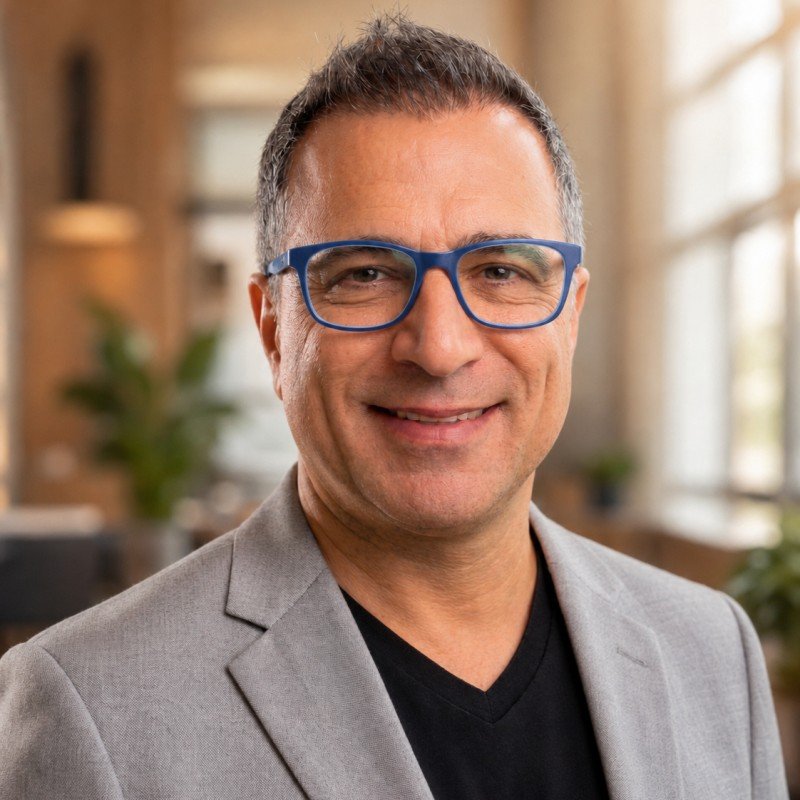
Trident Consulting Group is a team of experts led by founder Ross Ghiasi, a former Microsoft employee. Our team has advised 935+ customers, enabled 5,000+ users and deployed 9,300+ seats. We are based in Dallas, TX and work with organizations across the United States.
For background reading, see Agent governance: the missing layer in most enterprise AI, also available on LinkedIn.
Common questions
Who should own an AI agent?
Every agent gets a named business owner and a technical owner, plus a simple lifecycle from request through retirement. Nothing runs without someone responsible for it.
Does governance slow AI adoption down?
In our experience it does the opposite. When security, legal and business owners agree up front, approvals get shorter and pilots reach production.
Where should we start?
We begin with a free 30 minute call to understand which agents you already have, which are planned and where your concerns lie.
Does this work with the tools we already use?
Yes. We bring experience from real enterprise AI rollouts, including Microsoft Copilot and agent platforms, and we adapt the framework to the tools you already use.
Related services and reading
Keep exploring
Microsoft 365 Copilot enablement
Training, rollout and measurement so Copilot use keeps growing after launch.
Learn more ›
AI readiness assessment
A clear view of your data, security, access, workflows and people before you invest.
Learn more ›
Insights
All of our published writing on enterprise AI, grouped by topic.
Learn more ›
You can also see the full list of services and how we work on our homepage.
Ready to put governance in place?
Book a free 30 minute call. We talk about the agents you have, the ones you plan and what your security team needs to say yes.